Five Home Network Myths That Leave Your Front Door Wide Open
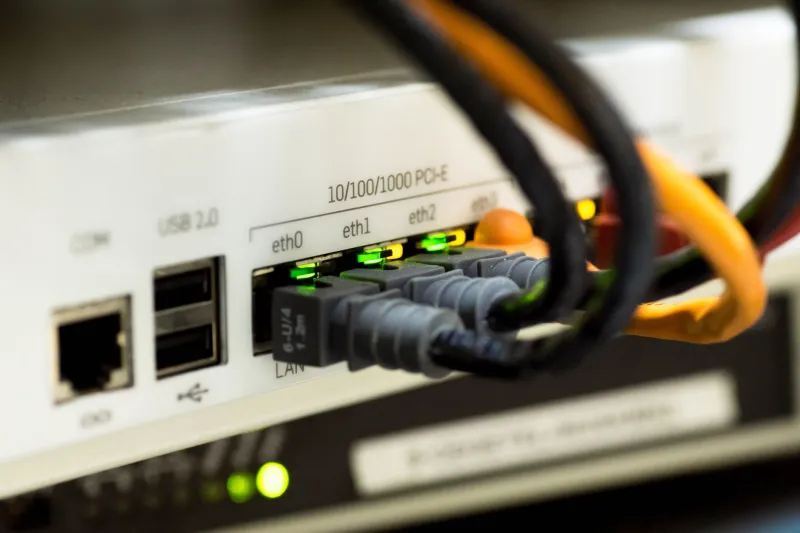
The American home network has quietly become the most attacked perimeter in domestic life. With remote work now standard for millions of households, the router in the hallway closet sits between a corporate network and whatever the neighborhood's scanning bots can reach. Yet most consumers treat it like a refrigerator: installed once, never thought about again.
CipherWatch examined the five most common misconceptions about home network security — each paired with the real-world consequence of believing it, and a fix that takes less time than a coffee refill.
Myth 1: "My Internet Provider Secures the Router"
ISPs provide the equipment; they do not defend it. Comcast, Spectrum, and AT&T all ship millions of gateways with remote management interfaces enabled, and default administrative credentials that appear on published lists within days of a hardware launch. Attackers scan entire IP ranges for routers still running factory passwords.
The fix: Change the administrator password the day the router is installed. Disable remote management (often labeled "Remote Access" or "CWMP") unless you genuinely use it. Both settings live in the router's admin page, typically reachable at 192.168.0.1 or 192.168.1.1.
Myth 2: "WPS Is a Convenient Feature"
Wi-Fi Protected Setup — the push-button pairing standard — has been cryptographically broken since a 2011 attack demonstrated that its eight-digit PIN could be brute-forced in hours. An attacker within radio range who presses nothing but a laptop can still find WPS-enabled routers that accept the attempt indefinitely.
The fix: Disable WPS entirely in the router settings. Modern devices connect via standard WPA2/WPA3 pairing just as easily; the button exists for a problem that ended a decade ago.
Myth 3: "My Wi-Fi Password Is Enough"
A strong WPA3 passphrase protects the radio link. It does nothing about what happens after a device joins. A compromised smart doorbell, a guest's malware-infected laptop, or a teenager's pirated game mod all land on the same flat network as your work laptop and home security camera. Lateral movement across a flat home network is among the most common stages of a residential intrusion.
The fix: Segment the network. Nearly every consumer router supports a guest network — a separate SSID with its own password and, crucially, its own subnet. Put every smart device, television, and visitor on it. Keep work machines and primary computers on the main network. Total time: under five minutes.
Myth 4: "Automatic Firmware Updates Are On By Default"
Some are; many are not. Routers from TP-Link, ASUS, and Netgear vary widely in update behavior, and older models — including many still actively sold at big-box retailers — stop receiving firmware entirely after three to five years. Unpatched routers are the single most exploited class of consumer device, feeding botnets like the long-running Mirai variants that have knocked portions of the American internet offline.
The fix: Check the update page today and enable automatic updates if offered. If the model is out of support, budget for replacement. A router is a security appliance with a shelf life, not furniture.
Myth 5: "Antivirus Covers the Network"
Endpoint protection watches the machine it is installed on. It cannot see an attacker intercepting traffic at the router, hijacking DNS settings to redirect banking sites, or exploiting the firmware of a device it will never touch. The 2024 surge in DNS-hijacking campaigns against consumer routers — changing settings without touching a single computer — is invisible to every antivirus product on the market.
The fix: Once a month, verify the DNS servers listed in your router's settings match what your ISP or a public resolver (such as 1.1.1.1 or 9.9.9.9) should be. Any unfamiliar entry is a red flag worth investigating immediately.
A Perimeter You Can Actually Defend
None of these steps requires technical expertise beyond reading a settings menu. Together they address the attacks that actually hit American households: credential scanning, WPS cracking, lateral movement, abandoned firmware, and DNS hijacking. The home network will never be a fortress. But it does not need to be one — it needs to be harder to enter than the neighbor's, and right now, for most households, it is not even close.